This page is more or less for myself, since not everything I did this year is worth it’s own blog, but I think it’s still worth keeping track so that when I look back at the year 2026, I won’t feel like I didn’t do anything.
- Found that a major Computer Peripheral manufacturer was leaking thousands of entries of customer data in their keyboard drivers whilst trying to configure my own keyboard
- Found a path traversal in the documentations page of a large IT Service Provider that leaked their internal documentation
- XSS across several software pieces, such as dify and also bypassing <redacted>’s WAF to get XSS
-
Found several vulnerabilities that lead to RCE in Woltlab, a Forum hosting software used by companies such as Hetzner, Netcup, Siemens, Deutsche Bahn and also some Austrian Government Agencies. Read the full blog here
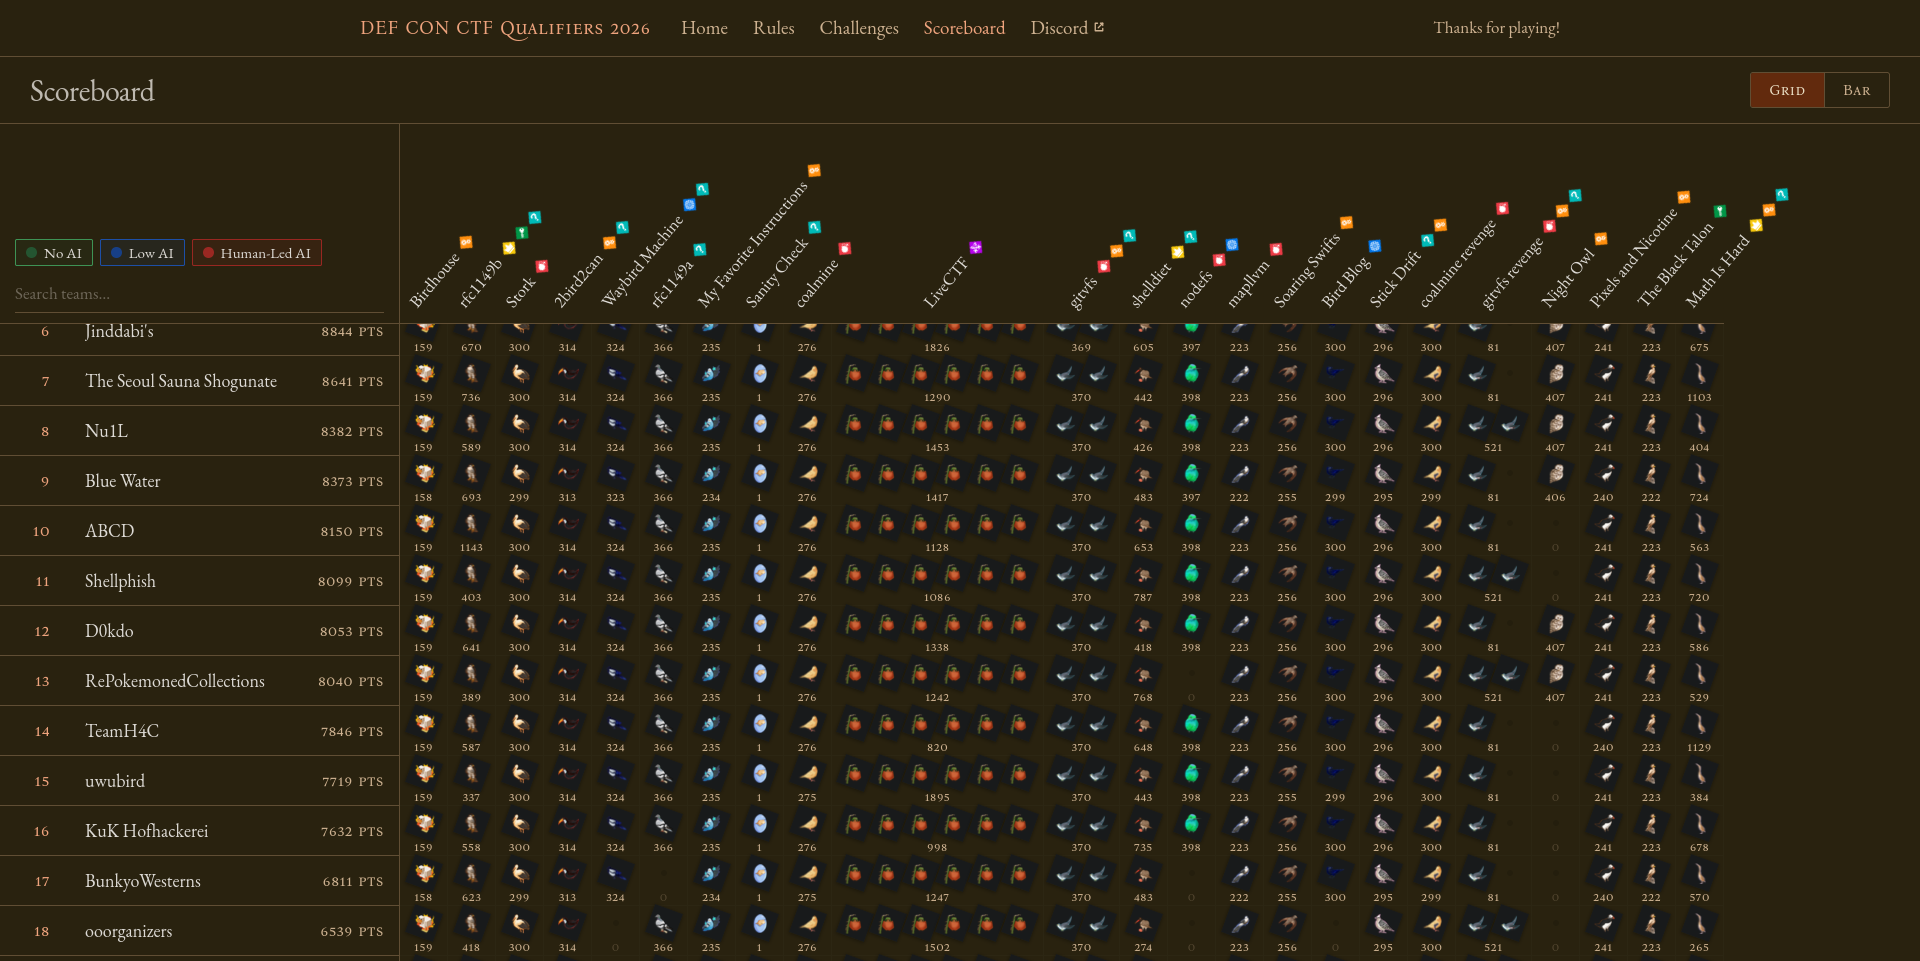
- 16th Place during DEFCON CTF Qualifications, while playing with KuK.
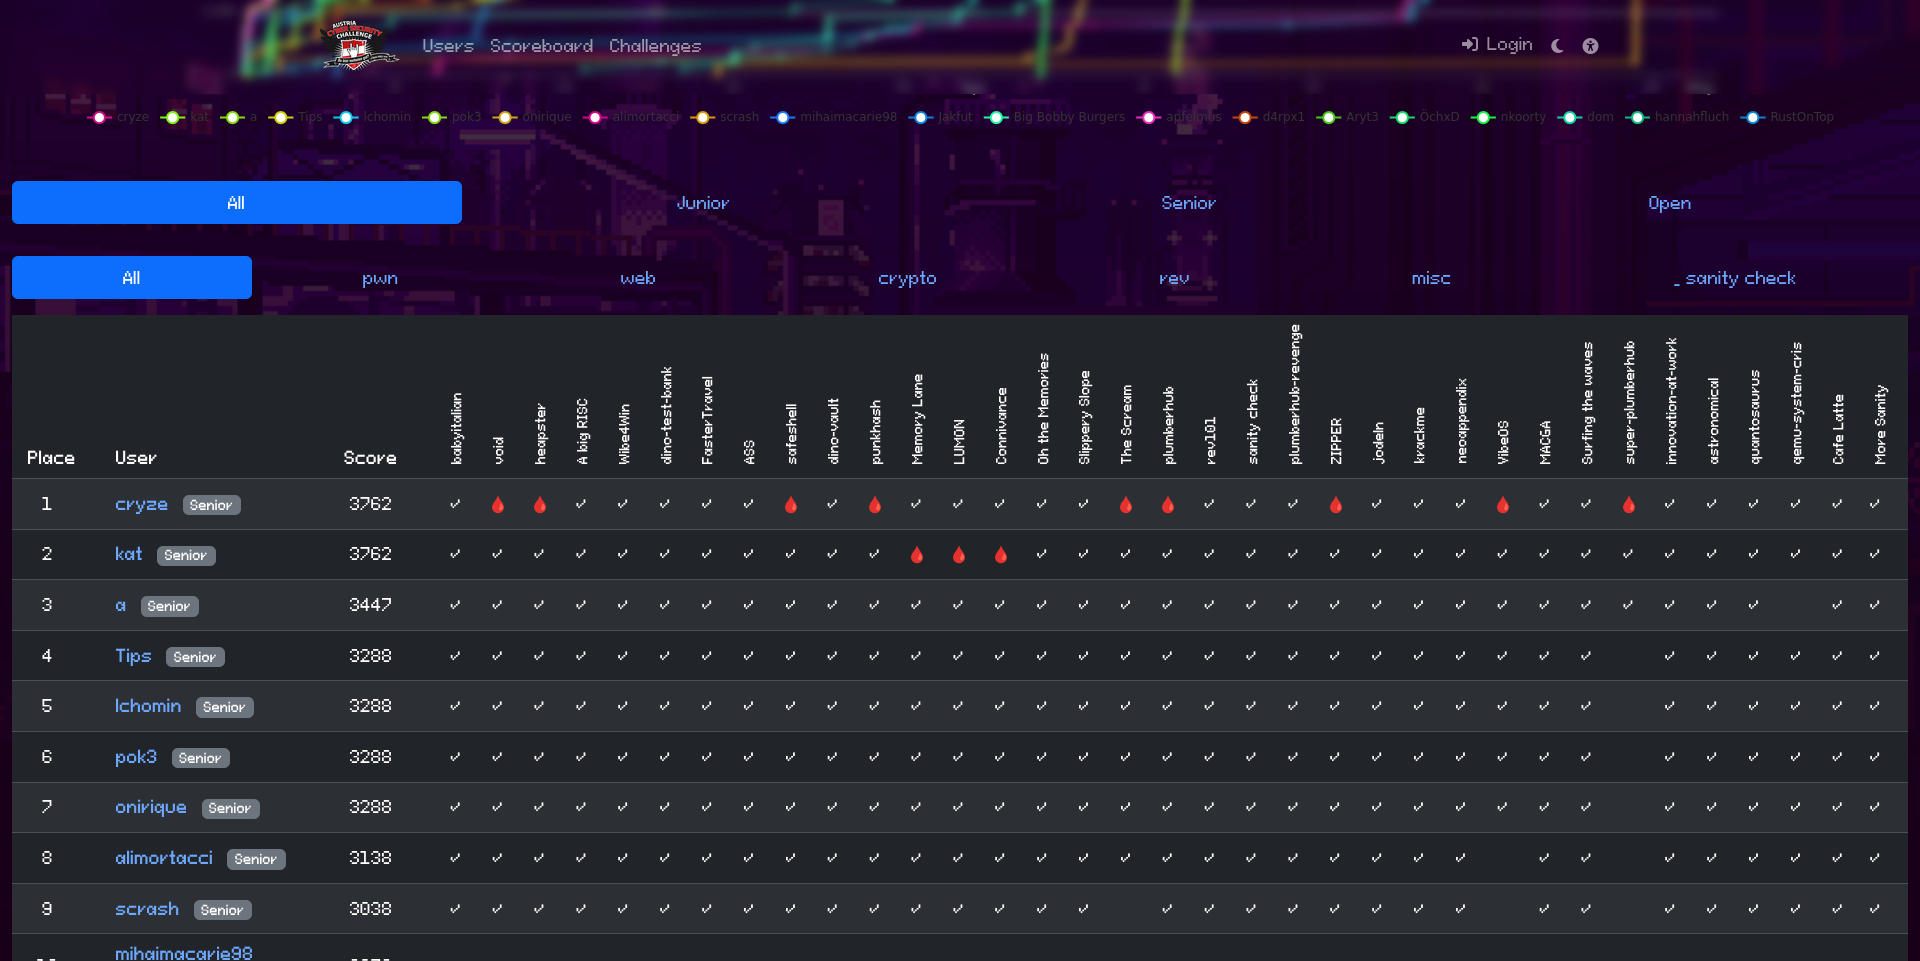
- 2nd Place during ACSC Qualifications
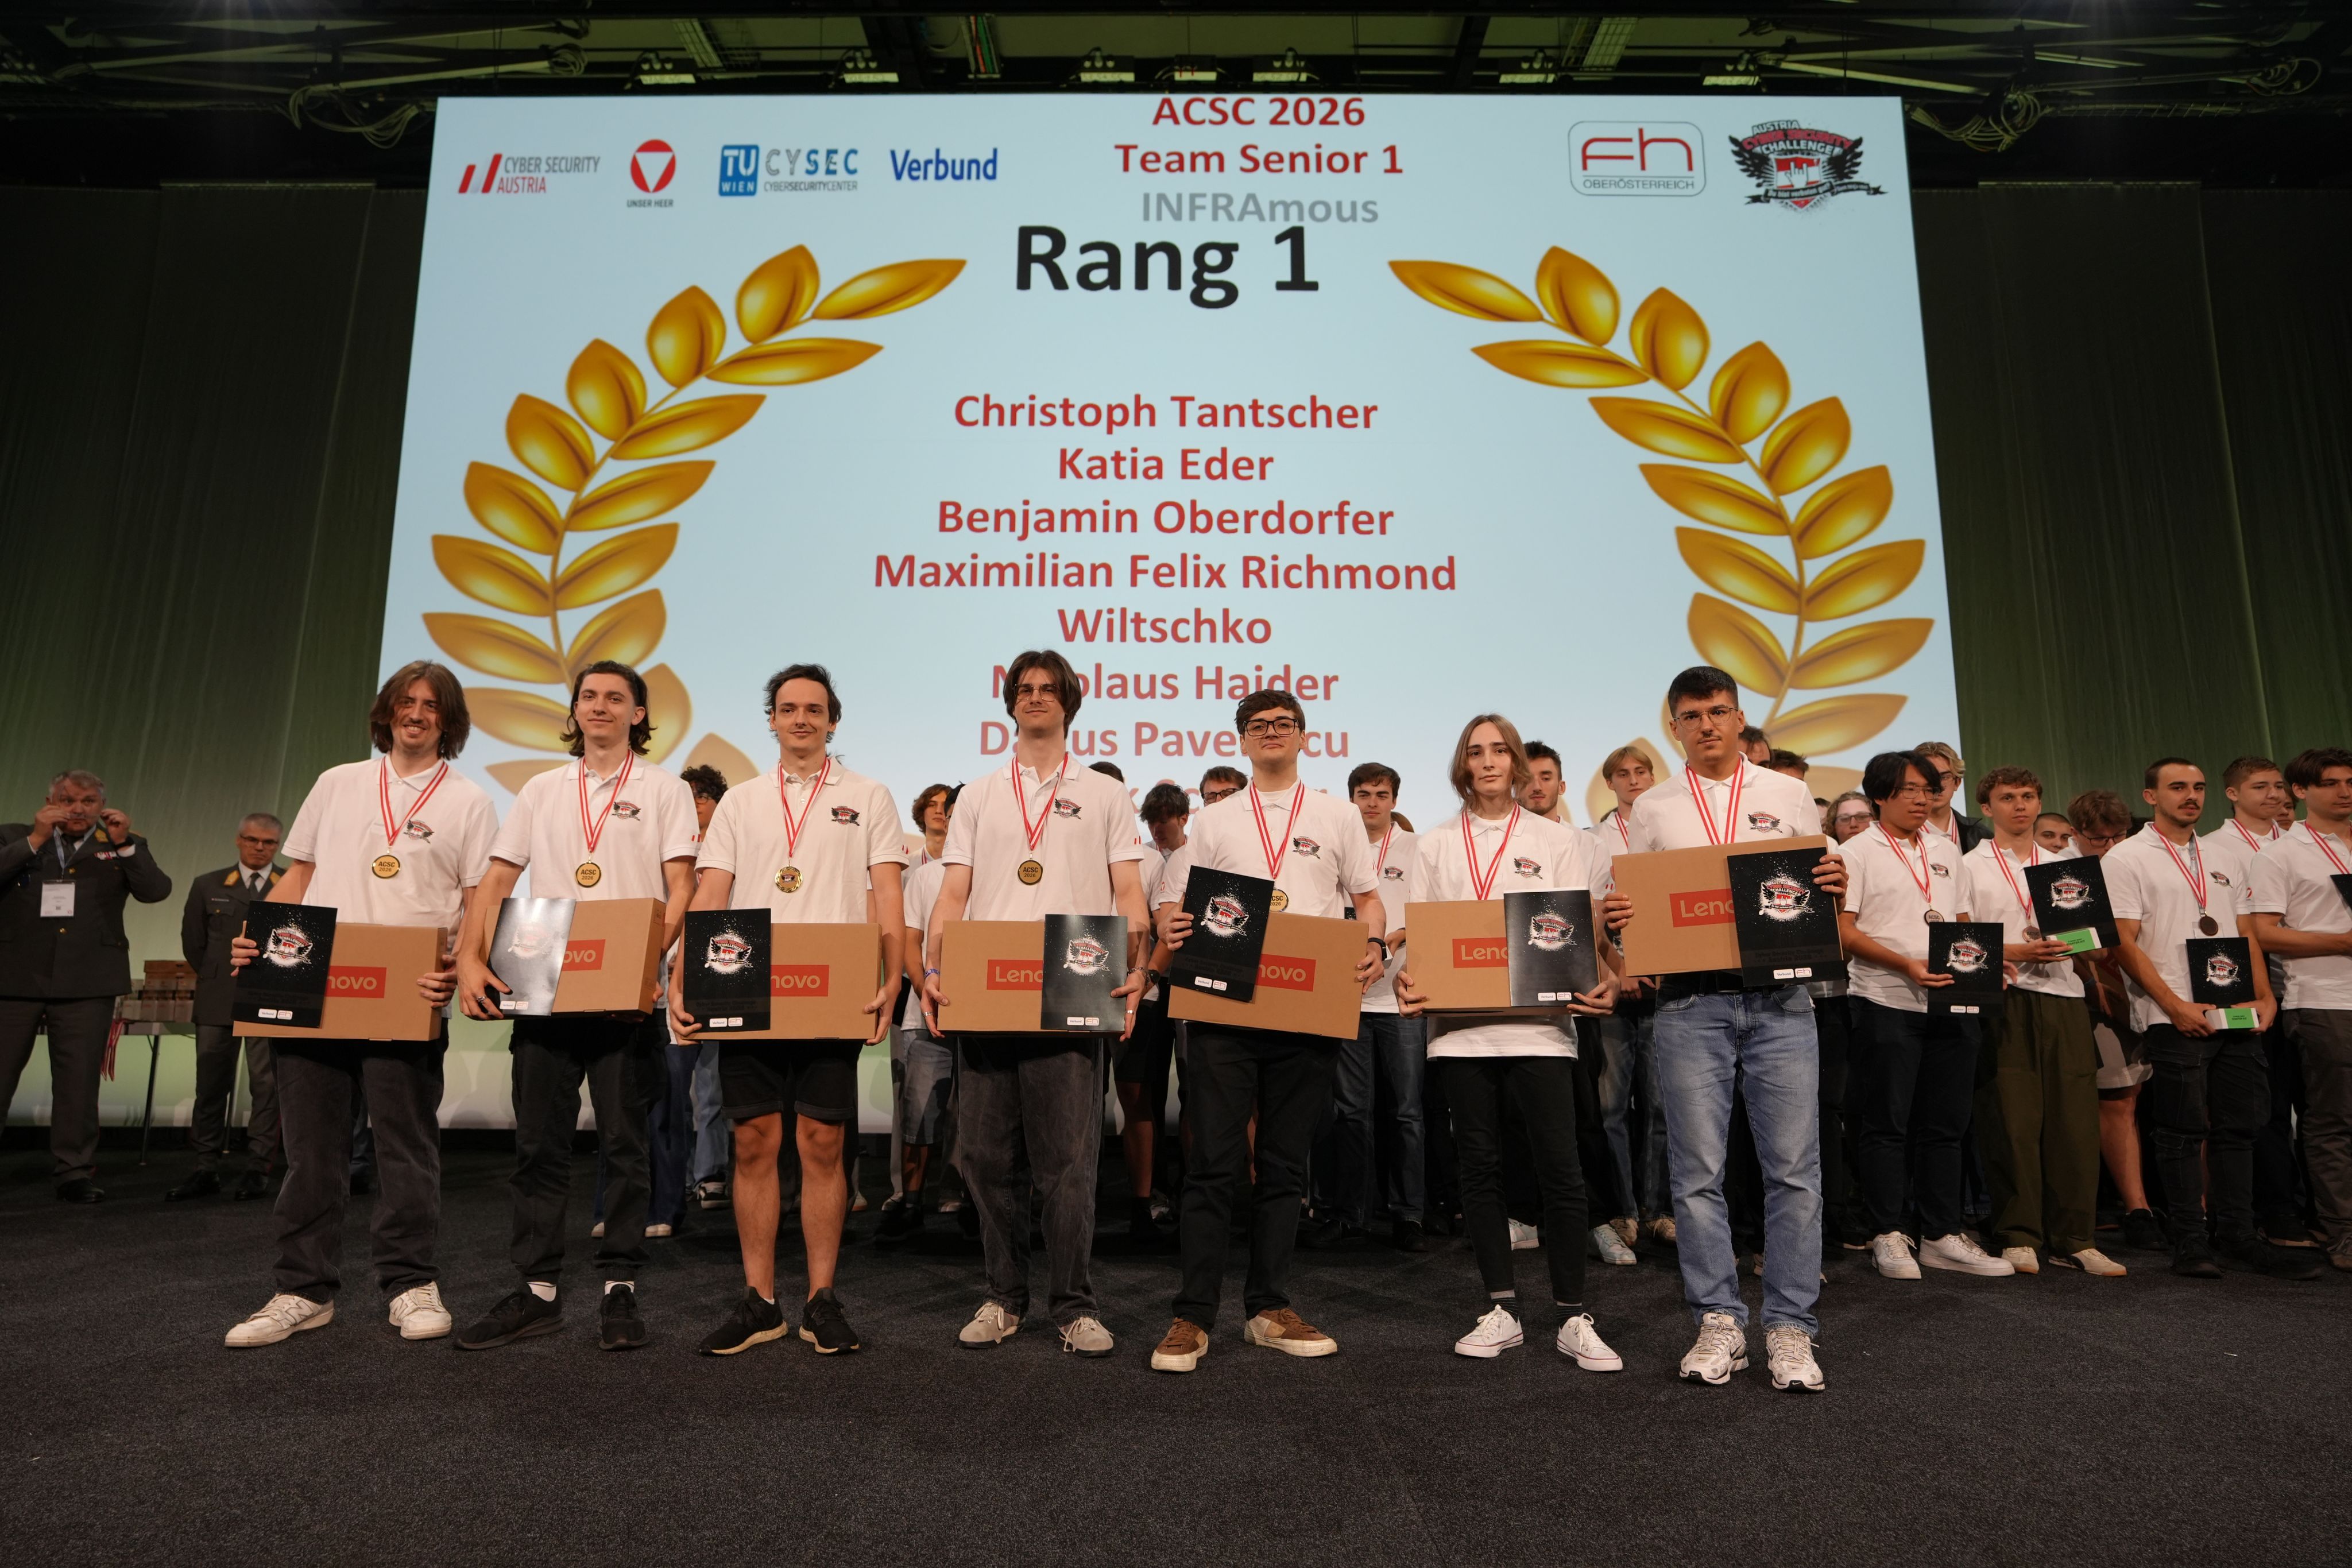
- 1st Place during ACSC Finals across both the Senior and Overall Scoreboard